AI Regulation in the US: One NIST-Based Governance Program for Every State
Texas is in force. Colorado and California follow on January 1, 2027. Federal preemption is still a proposal. One NIST-based program can meet all three.
Get the US template Book a strategy sessionAI regulation in the US is not one law. There is no comprehensive federal AI statute, and the states are writing their own rules on their own timelines. Texas is already in force. Colorado and California follow on January 1, 2027. Washington is debating whether to preempt them all.
For a private equity operating partner, that patchwork creates a practical question: does every portfolio company need a separate compliance program for every state? It does not. One governance program built on the NIST AI Risk Management Framework, mapped to each state's rules, can meet each regime and produce evidence that holds up in the data room.
This page sets out that operating model. It is the hub for our TRAIGA compliance guide, the AI Preemption Tracker and the US AI governance policy template. It is general information, not legal advice.
AI regulation in the US: the state patchwork in 2026
Three state regimes now define the compliance calendar for software companies selling into the US market. Each has a verified start date in its primary text.
| State | Law or rule | Takes effect | What it reaches |
|---|---|---|---|
| Texas | Texas Responsible AI Governance Act (TRAIGA), HB 149 | January 1, 2026 (HB 149 § 10) | Any person who promotes or conducts business in Texas, offers a product or service used by Texas residents, or develops or deploys an AI system in Texas (§ 551.002) |
| Colorado | SB 26-189, which repealed and reenacted Colorado's AI Act | January 1, 2027 (§ 5(1)) | Applies to decisions made on or after January 1, 2027 (§ 5(3)) |
| California | CPPA regulations on automated decisionmaking technology (ADMT) | Compliance by January 1, 2027 (Cal. Code Regs. tit. 11, § 7200(b)) | Businesses using ADMT covered by Article 11 (§§ 7200, 7220–7222) |
Colorado deserves a note. SB 26-189 replaced the original SB 24-205 framework, and the replacement is now the subject of litigation and proposed Attorney General rules. We track that position, as of the court's most recent verified order, on the AI Preemption Tracker.
What each regime asks of a software company
Texas is built around prohibited uses and intent. Most of its private-sector prohibitions turn on what a developer or deployer intended, such as an AI system developed with the intent to unlawfully discriminate against a protected class (§ 552.056). Enforcement sits with the Attorney General alone, and a 60-day cure period comes before any penalty for a curable violation (§ 552.104).
Colorado and California regulate automated decision-making. Before 2027, any product that automates decisions about people, such as hiring, lending or eligibility, should be checked against each regime's scope definitions. A Texas-ready program that records intended purpose, testing and human review gives both 2027 regimes a head start.
The lesson for a portfolio is timing. A company that builds its program for Texas in 2026 has roughly a year to extend the same evidence to Colorado and California before both regimes start.
Federal AI regulation in the US: proposals, not statutes
At the federal level, AI regulation in the US is still executive action and proposals. None of it is a statute that displaces the state dates above.
- Executive Order 14365 (signed December 11, 2025; 90 FR 58499) directs a Department of Justice AI Litigation Task Force, a Commerce evaluation of state AI laws, and follow-on steps by NTIA, the FCC and the FTC.
- The DOJ AI Litigation Task Force was established by Attorney General memorandum on January 9, 2026.
- The FTC's proposed policy statement on AI (91 FR 41638, July 7, 2026) took comments until July 31, 2026.
- The White House legislative framework (March 2026) recommends that "Congress should preempt state AI laws that impose undue burdens", while keeping state laws of general applicability, such as child-protection, fraud and consumer-protection laws.
Recommendations to Congress are not law. Until Congress acts or a court rules, the state dates stand.
For a portfolio company, the federal track matters in two ways. First, the FTC already enforces Section 5 of the FTC Act against unfair or deceptive practices, and its proposed AI statement signals how that power may be applied to AI outputs. Second, a federal standard, if one arrives, is likely to sit closer to NIST than to any single state. A program built on NIST is the smallest step to whatever comes next.
Executive action can change the enforcement climate. It does not change a statute's effective date. Plan to the state calendar and watch the federal track.
Why NIST is the common denominator
The NIST AI Risk Management Framework (AI RMF 1.0, released January 26, 2023) is intended for voluntary use. It organizes AI risk work into four core functions: GOVERN, MAP, MEASURE and MANAGE. Its Generative AI Profile, NIST AI 600-1 (released July 26, 2024), applies those functions to generative systems.
Voluntary does not mean irrelevant. Texas wrote NIST into its liability safe harbor. Under Tex. Bus. & Com. Code § 552.105(e)(2)(D), a defendant is not liable where it discovers a violation through substantial compliance with the most recent version of the NIST Generative AI Profile, or another nationally or internationally recognized AI risk management framework, together with an internal review process.
For AI regulation in the US, that gives a multistate program a legal anchor, not just a best-practice argument. Build on NIST once, and the same controls support the Texas safe harbor while giving you a structured basis for Colorado and California.
How the four functions become evidence
- GOVERN: an approved AI policy, named owners, and a board reporting line. Evidence: policy, RACI and board minutes.
- MAP: each AI system's context, intended purpose and affected people. Evidence: the AI system register and screening records.
- MEASURE: testing for accuracy, bias and misuse, including adversarial or red-team testing. Evidence: test plans and results.
- MANAGE: treatment of the risks found, incident response and change control. Evidence: risk register, human-review logs and incident records.
Mapped this way, NIST stops being a reading list and becomes a set of documents an auditor, acquirer or regulator can inspect.
Which NIST versions this framework maps to
NIST states that the AI RMF 1.0 "is being revised". This framework maps to AI RMF 1.0 (January 2023) and AI 600-1 (July 2024), and is reviewed quarterly, or sooner if NIST publishes a revision.
The architecture: US Core, State Modules, Preemption Tracker
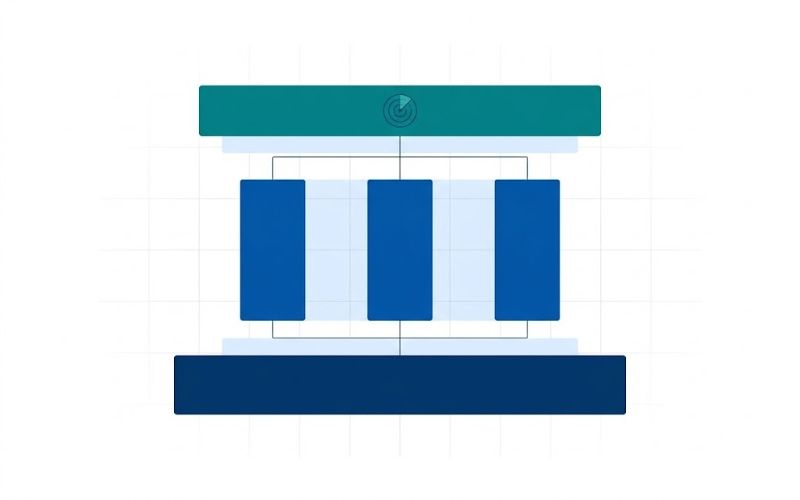
The framework has three layers, so a portfolio company does the shared work once and adds only what each state requires.
- US Core. The NIST-based foundation: AI system inventory, intended-purpose records, risk assessment, testing, human review and vendor management. Every company in the portfolio runs it.
- State Modules. Thin overlays that map each state's specific obligations onto the US Core. Texas is live; Colorado and California follow ahead of their 2027 dates.
- Preemption Tracker. A monthly watch on federal action, so the program adapts if Congress or the courts change the landscape.
Every obligation runs through the same row schema, which keeps the evidence consistent across states and easy to audit:
ObligationNIST AI RMF subcategoryAI 600-1 actionISO/IEC 42001 Annex A controlevidence artifactownerreview cadence
The controls are aligned with ISO/IEC 42001, the AI management system standard. Alignment means the evidence maps to its Annex A controls; it is not a certification claim.
A worked Texas example
| Field | Entry |
|---|---|
| Obligation | Do not develop or deploy an AI system with the intent to unlawfully discriminate against a protected class (§ 552.056) |
| NIST AI RMF | MEASURE: bias and fairness testing; GOVERN: documented intended purpose |
| AI 600-1 action | Pre-deployment testing and documented review of outputs |
| ISO/IEC 42001 | Annex A impact-assessment control (aligned, not certified) |
| Evidence | Intended-purpose record, bias test results, sign-off |
| Owner | Product lead, with legal review |
| Review cadence | Each major release and at least annually |
Colorado and California rows reuse the same evidence and add only their own triggers and notices.
State modules at a glance
Texas — live
TRAIGA is in force from January 1, 2026, with exclusive Attorney General enforcement, a 60-day cure period and the NIST-linked safe harbor. Read the full TRAIGA compliance guide.
Colorado — coming 2027
SB 26-189 takes effect January 1, 2027. The module will follow the final Attorney General rules and the outcome of current litigation.
California — coming 2027
The CPPA's ADMT compliance date is January 1, 2027. The module will map Article 11 to the US Core.
Start with the template. Download the US AI governance policy template (NIST AI RMF + TRAIGA) and run the 10-item checklist against one portfolio company this week.
Get the US templateEvidence you can defend in the data room
Wherever AI regulation in the US lands, buyers, lenders and regulators ask the same question in different words: show me. A defensible program produces six artifacts.
- AI system register with each system's intended purpose and owner.
- Prohibited-use screening record against the Texas prohibitions (§§ 552.052–552.057).
- Risk and profiling assessments, including Texas data protection assessments where profiling triggers § 541.105(a)(3) of the Texas Data Privacy and Security Act.
- Human-review logs showing who reviewed which decisions and when.
- Vendor contracts with AI-specific terms on testing, data use and incident notice.
- AG inquiry and cure readiness: a named owner and a playbook for the 60-day cure period under § 552.104.
Each artifact maps to a row in the crosswalk. That is the difference between a policy binder and a program: the binder states intent; the program proves it.
In practice, these six artifacts answer the questions a buyer's diligence team actually asks: which AI systems do you run, what are they for, how did you test them, who reviews their outputs, what do your vendors promise, and what happens if the Attorney General writes to you? A company that can answer all six in a day has a governance program. One that needs a month has a project.
Federal laws that already apply to AI
New AI statutes sit on top of laws that already reach automated systems. Keep these in the US Core:
- FTC Act § 5: unfair or deceptive acts or practices (15 U.S.C. § 45(a)(1)).
- HIPAA Privacy and Security Rules (45 CFR Parts 160 and 164).
- FCRA adverse-action notices (15 U.S.C. § 1681m).
- ECOA statements of specific reasons for credit denials (15 U.S.C. § 1691(d)).
- Title VII disparate-impact liability in employment (42 U.S.C. § 2000e-2(k)).
None of these is new, which is the point. A program that only tracks AI-specific laws misses the obligations most likely to be enforced first.
How AI regulation in the US changes the board agenda
For a PE-backed software company, AI governance is now a value question as much as a compliance one. A clean register and evidence pack shorten diligence, reduce indemnity friction and give the board a clear view of where AI creates risk and where it creates margin.
It also changes who owns the work. The program needs an executive owner, usually the CEO, CTO or a fractional Chief AI Officer, with legal, product and security each holding named rows in the crosswalk. Quarterly board reporting keeps it current as the state calendar moves.
Putting the program in place: a 90-day path
- Days 1–30: inventory and screen. Build the AI system register, record intended purposes, and screen every system against the Texas prohibitions.
- Days 31–60: assess and test. Run risk and profiling assessments, start adversarial testing on the highest-risk systems, and set up human-review logging.
- Days 61–90: assign and evidence. Name owners for every crosswalk row, update vendor terms, rehearse the 60-day cure process, and present the evidence pack to the board.
At day 90, the company has a working US Core and a live Texas module, and the Colorado and California modules become an extension rather than a rebuild.
That is why we position governance as something you can defend in the data room, in any state. Australia and EU coverage lives on our Australian and EU AI governance framework.
Frequently asked questions
Is there a federal AI law in the US?
No. There is no comprehensive federal AI statute. Federal activity so far is executive action and proposals: Executive Order 14365 (December 11, 2025) directs agency reviews and a DOJ task force, and the White House's March 2026 framework asks Congress to preempt state AI laws that impose undue burdens. Until Congress legislates, state laws such as Texas TRAIGA apply on their own terms.
Does an executive order override state AI laws?
Not by itself. Executive Order 14365 directs federal agencies and the Department of Justice to act, including challenging state AI laws in court, and the White House has asked Congress to enact preemption by statute. State effective dates stand unless Congress legislates or a court rules otherwise. Our AI Preemption Tracker records each federal step against its primary source. This is not legal advice.
Is the NIST AI RMF mandatory?
No. NIST describes the AI Risk Management Framework as intended for voluntary use. It still matters legally: Texas TRAIGA gives a liability safe harbor to a defendant that discovers a violation through substantial compliance with the most recent NIST Generative AI Profile, or another recognized framework, together with an internal review process. Building on NIST therefore supports compliance in Texas.
Should AI governance be a board-level issue?
For PE-backed companies, yes. AI governance now affects diligence, valuation and exit readiness as well as compliance. A board that sees a current AI system register, risk assessments and human-review evidence can answer buyer and lender questions quickly. Treat the evidence pack as a standing board item, reviewed quarterly, rather than a one-off legal project.
Why is AI compliance getting more complex in 2026?
Because the calendar is filling up. Texas TRAIGA took effect on January 1, 2026. Colorado's SB 26-189 and California's ADMT regulations both start on January 1, 2027. At the same time, federal action under Executive Order 14365 is still unfolding. Companies selling across states need one program that adapts to each regime instead of separate projects.
Next step
Download the US AI governance policy template, or book a 30-minute AI strategy session to map one portfolio company against the Texas module.
Get the US template Book a strategy sessionGeneral information only; not legal advice. Texas counsel review is recommended before relying on any statutory summary.